Key takeaways
- Scope is narrower than most guides say. GDPR reaches you through an EU establishment or by monitoring people in the EU. Recruiting alone does not trigger it.
- An EOR does not take your duties. Roles follow who decides why data is used, so expect a split between you and the EOR, written into the data processing agreement.
- Every record needs a deletion date. GDPR sets no fixed period. For rejected candidates, 6 to 12 months is the range commonly advised.
- Employer fines are real. The CMS tracker records 191 employment fines averaging about €1.9 million, against a cap of €20 million or 4% of turnover.
Our take
Transfer law gets the headlines, but employer fines keep landing on legal basis, transparency and vendor security. Fix those three first, then do the transfer paperwork.
Manjuri Dutta, Co-Founder & Editor, EmployerRecordsDoes GDPR apply when you hire in the EU?
It applies in two cases, and a CV alone is neither. GDPR covers you if you have an establishment in the EU, or if you monitor the behaviour of people while they are in the EU.
The EDPB’s territorial scope guidelines treat paying and administering staff as employment administration, not an offer of services. Their examples include a US company with staff on EU business trips and a Monaco company paying French and Italian employees. Neither is caught on that basis.
Check Article 27. A non-EU company that falls under the monitoring limb usually needs an EU representative. The only exemption is processing that is occasional, low risk and free of large-scale sensitive or criminal data.
Who is the controller when you use an EOR?
It depends on the data, not the label on the contract. GDPR defines the controller as whoever decides why and how personal data is processed, so each party’s role follows what it actually decides.
In an EOR hire the split is usually mixed. Before the EOR is engaged, you control candidate data. Once the EOR is the legal employer, it sets its own purposes for payroll, statutory filings and employment records, which makes it a controller for that processing. Provider documents describe this differently, so read the data protection terms, not the marketing page. If the model is new to you, start with what an employer of record is.
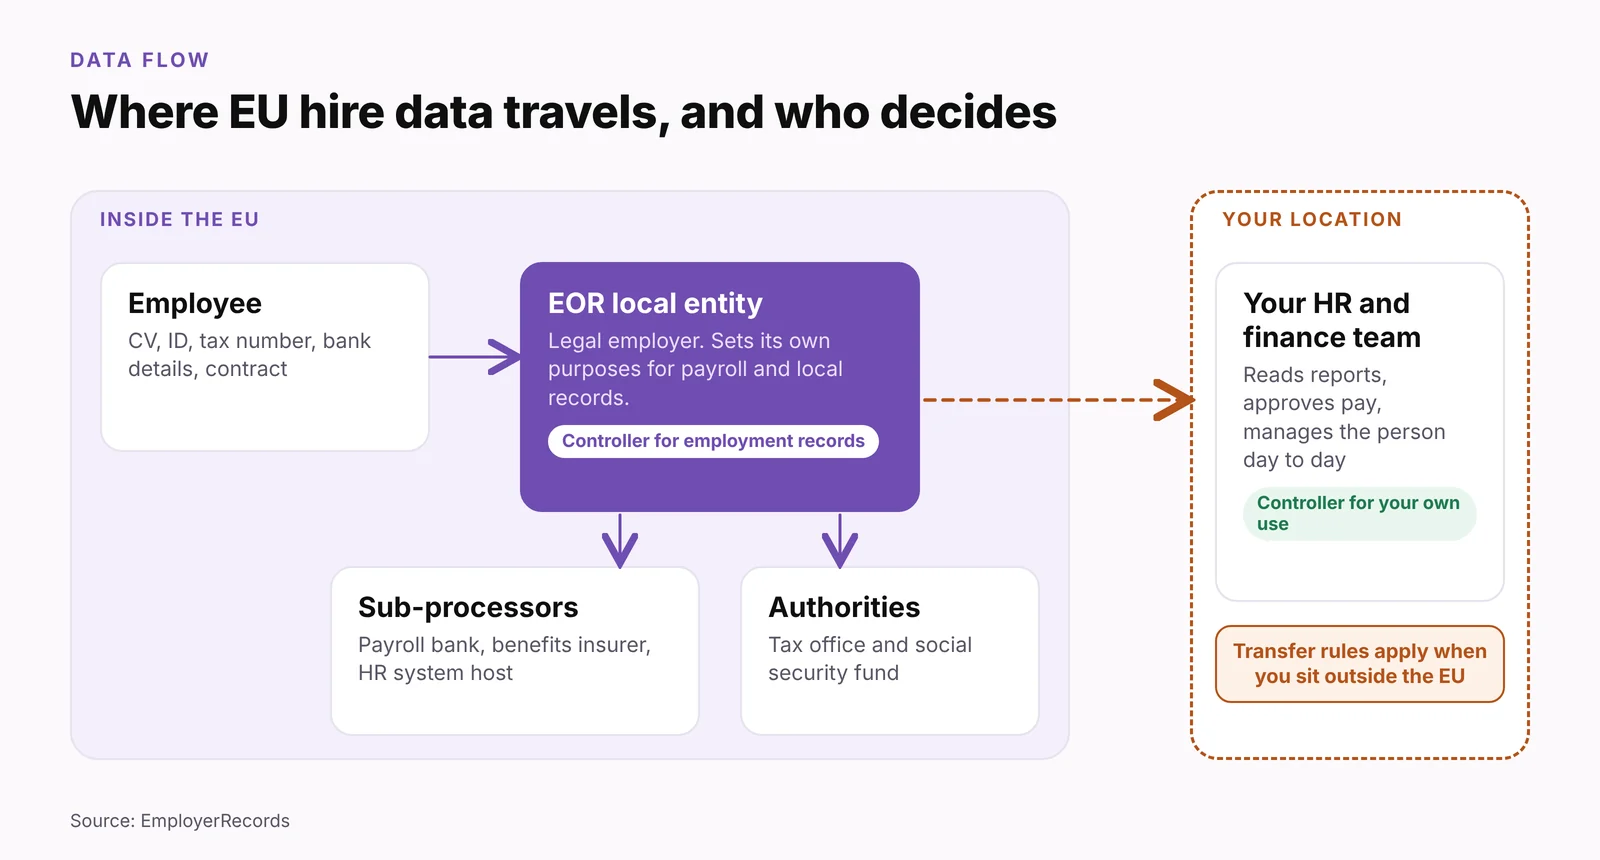
You usually decide
- Which candidates you collect data on, and why
- How you use performance and work data after hire
- Which tools you add on top of the EOR’s systems
- Whether data is sent to teams outside the EU
The EOR usually decides
- Payroll, tax and social security filings
- Employment records the local law requires
- Benefits administration with insurers
- Retention under local employment and tax law
Labels do not settle it. A processor that sets its own purposes becomes a controller for that processing. Where both sides set purposes together, Article 26 requires a written joint controller arrangement.
Which legal basis covers each hiring step?
Contract necessity and legitimate interests cover most hiring steps, and consent rarely does. Employer and candidate are not equal parties, so consent is hard to show as freely given, and withdrawing it must never cost the candidate anything.
Legal basis by hiring step
| Hiring step | Usual basis | Limit that applies |
|---|---|---|
| Reviewing a CV and application form | Steps before a contract | Only data needed to assess the application |
| Keeping a rejected candidate in a talent pool | Consent | Separate, optional and easy to withdraw |
| Reference checks on a shortlist | Legitimate interests | Documented balancing test; the candidate can object |
| Criminal record checks | National law only | Article 10 allows them only where law authorises them |
| AI scoring or ranking | Depends on the tool | Article 22 and a DPIA apply, see the AI section |
How long can you keep candidate data?
GDPR sets no fixed period: data must go once its purpose ends. For rejected candidates, 6 to 12 months is the range commonly advised, long enough to answer a challenge and no longer. France is more generous: the CNIL’s recruitment guidance allows two years after last contact if the candidate is told and does not object.
Hired candidates’ records move into the employee file, and retention then follows local employment and tax law, which differs by country. Check the country’s hiring guide, for example hiring in France.
Enforce deletion in the applicant tracking system, not in a policy document. Interview notes, emails and spreadsheets count as candidate data too.
How fast must you answer a data request?
You have one month for an access request, and 72 hours to tell the regulator about a notifiable breach. A plain email asking what you hold is a valid request.
The deadline covers every system: the ATS, email, interview notes and the EOR’s records. Erasure is not absolute, since you may keep data you need to defend a legal claim. Your EOR contract should set a time limit, measured in days, for passing on requests it receives. Fine tiers are set out in Article 83.
How do you move EU data to another country?
Use the first mechanism that applies: an adequacy decision, then a certified recipient under the Data Privacy Framework, then Standard Contractual Clauses with a transfer impact assessment. Large groups can use Binding Corporate Rules for internal flows.
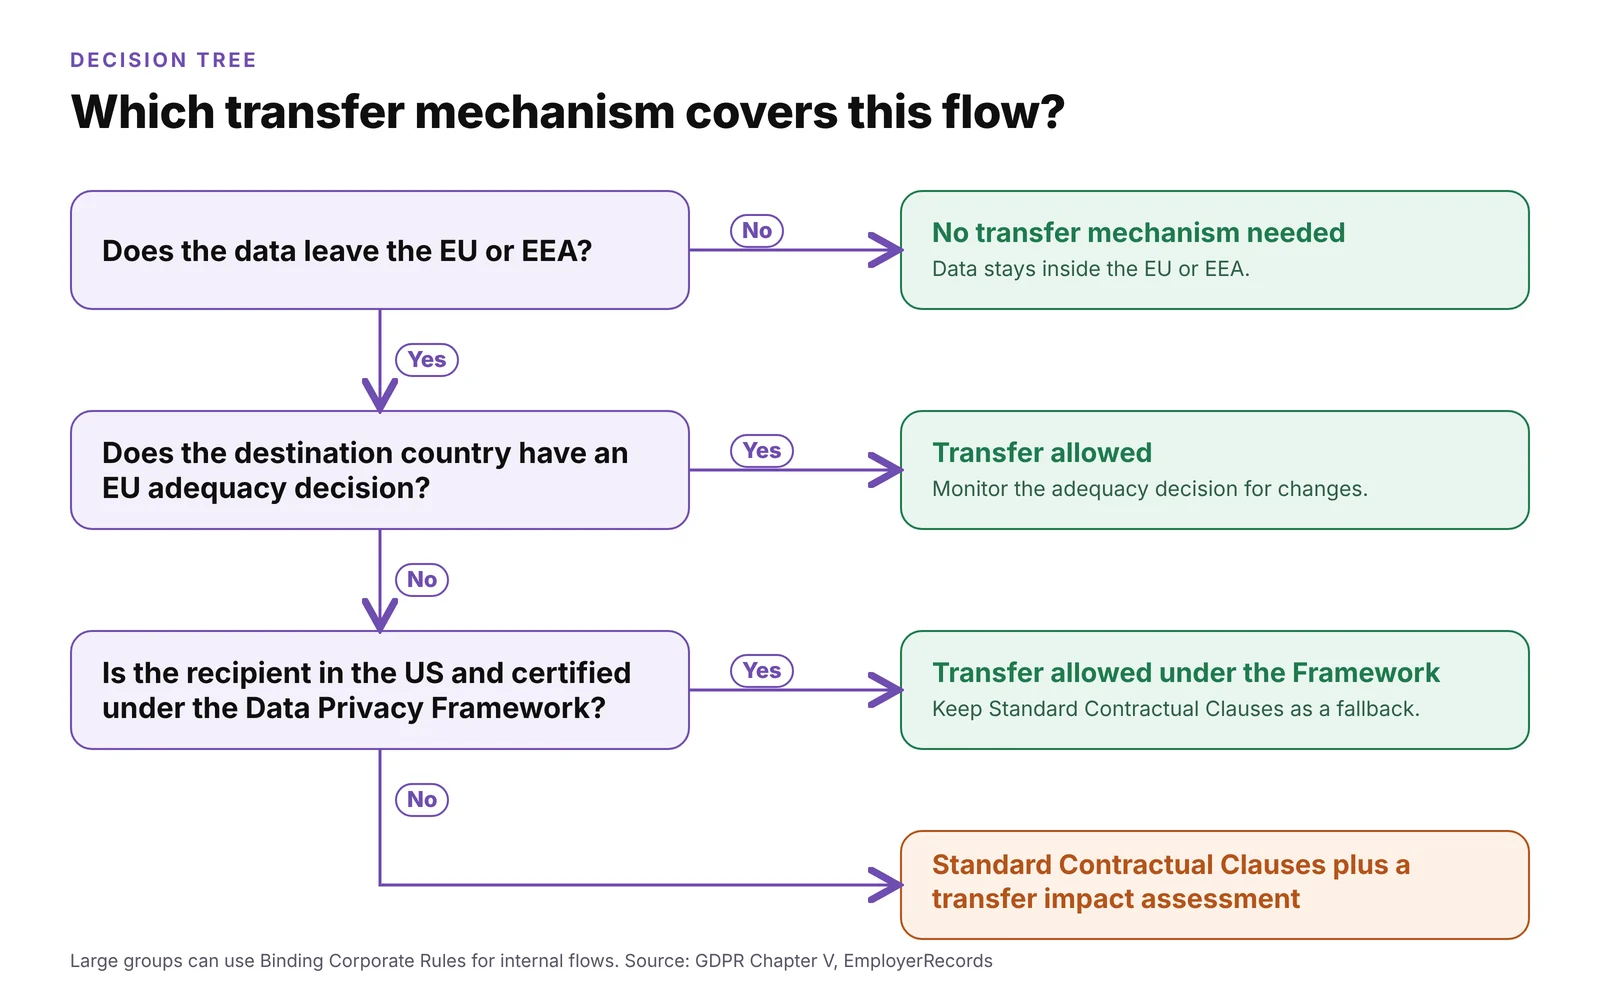
Sending a hired employee’s records to a payroll or HRIS team outside the EU is a transfer too, so map where the EOR’s data ends up. The status of the main routes, as at 3 November 2026:
Where the main transfer rules stand
| Route | Status | What it means |
|---|---|---|
| EU to US, Data Privacy Framework | Current | In force. The General Court upheld it on 3 September 2025 and the appeal (C-703/25 P) is pending, so keep Standard Contractual Clauses as a fallback for large flows. |
| EU to UK, adequacy | Current | Renewed in December 2025 until 27 December 2031, with possible further renewal. |
| EU and Brazil, adequacy | Current | Mutual adequacy decisions were adopted on 27 January 2026. |
| GDPR changes in the Digital Omnibus | Pending | The data part still awaits a Council mandate and a Parliament vote, so current GDPR text applies. |
Which EU countries add rules on top of GDPR?
Several do, because member states can add employee data rules under Article 88. Works councils in Germany and the Netherlands often decide which HR tools you can switch on. Our research tracks 180 employer rule changes in 2026 across countries.
What four markets add to GDPR
| Country | What it adds |
|---|---|
| Germany | Works council co-determination under section 87(1) no. 6 BetrVG for technical tools suited to monitoring staff. The Court of Justice held in C-34/21 that section 26 BDSG may be disapplied where it adds no specific safeguards, so Article 6 GDPR applies directly. |
| Netherlands | Works council consent under Article 27 of the Works Councils Act for data processing involving employees. |
| France | CNIL guidance requires candidates to be told who receives their data, any transfers and the recruitment tools used. |
| Poland | Labour Code Article 22(1) limits what a candidate can be asked for: name, date of birth, contact details, education and, where the role needs it, qualifications and work history. Consent cannot widen the list. |
Other member states add their own rules. Confirm local requirements before launching a tool in a new country.
How do AI screening tools change the rules?
Article 22 restricts decisions based solely on automated processing that significantly affect a person, and rejection from a role qualifies. A recruiter who approves every output without review does not remove the automation.
The EU AI Act treats hiring tools as high risk. Regulation 2026/1744 moved those obligations from August 2026 to 2 December 2027, so they are scheduled, not yet in force. Prohibitions and AI literacy duties already apply, and so does GDPR.
What do employment fines look like?
The CMS enforcement tracker report records 191 fines tied to employee data, worth about €360.8 million in total. The report flags weak legal basis and poor transparency as the main hotspots.
Employment enforcement cases
| Case | Fine | Failure |
|---|---|---|
| H&M, Hamburg authority, 2020 | €35.3M | Excessive monitoring of employees’ personal details in a service centre |
| Mobility provider, Dutch authority, 2024 | €290M | Drivers’ data transferred to the US without adequate safeguards |
| McDonald’s Polska, Polish authority, 2025 | €4.0M | Weak security at a scheduling processor led to a breach |
| PwC Greece, Greek authority, 2019 | €150,000 | Unlawful basis for processing employee data |
The McDonald’s Polska case matters for EOR users: the fine fell on the controller for a processor’s weak controls. Vendor oversight is your liability.
What should you ask an EOR about data protection?
Ask six questions before signing, and get the answers into the data processing agreement. Our guide to choosing the right EOR covers the wider checks.
Which data do you handle as controller, and which as processor?
Listen for an answer by data type, not one label for everything.Who are your sub-processors, and where is data stored?
You need the full list and notice before it changes.Which mechanism covers data sent to my team outside the EU?
Expect Standard Contractual Clauses or Data Privacy Framework certification, plus a transfer assessment.How fast do you pass on access and deletion requests?
Look for a contractual limit measured in days.How quickly will you tell me about a breach?
You may have 72 hours to notify the regulator, so notice must come well inside that.What happens to our data when the contract ends?
Article 28 requires deletion or return.Questions about GDPR in global hiring
Short answers to what employers ask most, checked against the EDPB guidelines, the CMS enforcement tracker and EU court records on 3 November 2026.
Does GDPR apply to a non-EU company hiring in the EU?
Only if it has an EU establishment or monitors the behaviour of people while they are in the EU. The EDPB guidelines treat recruiting and paying staff as employment administration, not an offer of services, so a CV alone does not bring a non-EU company in.
Is an EOR a data controller or a processor?
Often both, depending on the data. The EOR is the legal employer and sets its own purposes for payroll and local filings, which makes it a controller for that processing, while it may act as your processor for tasks you instruct. Settle the split in the data processing agreement.
How long can you keep rejected candidates’ CVs?
GDPR sets no fixed period. For rejected candidates, 6 to 12 months is the range commonly advised, and the CNIL’s guidance in France allows two years after last contact if the candidate is told and does not object.
Can you rely on candidate consent?
Rarely for core hiring steps, because the power gap between employer and candidate makes consent hard to show as freely given. It works for optional extras such as talent pool membership, if withdrawal is easy and carries no penalty.
Is the EU-US Data Privacy Framework still valid?
Yes, it remains in force. The General Court dismissed the challenge in Latombe on 3 September 2025, and the appeal (C-703/25 P) is pending at the Court of Justice, so keep Standard Contractual Clauses as a fallback for large transfers.
Do you need an EU representative?
Article 27 requires one for non-EU controllers and processors that fall under the monitoring limb, unless the processing is occasional, low risk and avoids large-scale sensitive or criminal data. Having a representative does not create an EU establishment.
When do the EU AI Act hiring rules apply?
Hiring tools are high risk under the AI Act, and Regulation 2026/1744 moved those obligations to 2 December 2027. Prohibitions and AI literacy duties already apply, and GDPR Article 22 applies to automated decisions now.
How much can an employer be fined under GDPR?
The upper tier is €20 million or 4% of worldwide annual turnover, whichever is higher, and the lower tier is €10 million or 2%. In employment cases, the CMS tracker report records 191 fines averaging about €1.9 million.
About the author
Manjuri Dutta is Co-Founder and Content Editor at EmployerRecords.com, covering Employer of Record providers and global hiring platforms. She evaluates providers on entity ownership, statutory compliance, and real pricing rather than vendor claims, and built the verification process used across EmployerRecords' country guides, checking vendor claims against government registries and public filings.
View all articles by Manjuri